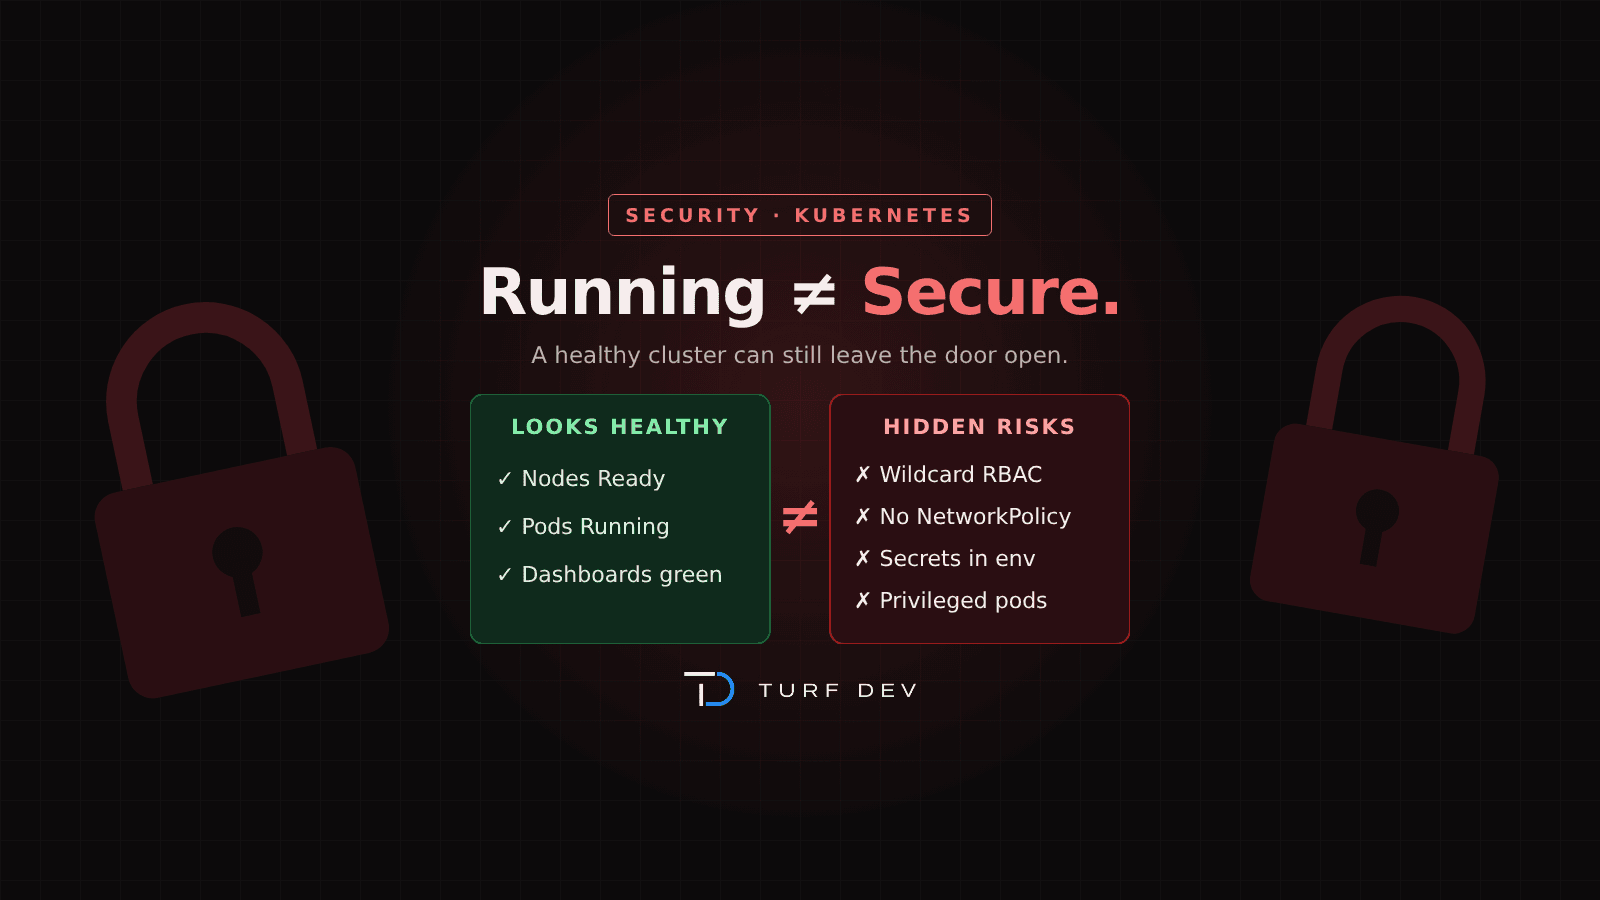
Your Kubernetes Cluster Is Running. But Is It Secure?
Six practical checks to uncover security gaps in a running Kubernetes cluster, from image scanning and RBAC to Secrets, policy enforcement and runtime detection.
Author
Founder & CEO, Turf Dev
Aditya began his career as a paleoclimatologist, earning two research fellowships for his contributions to the study of Earth's ancient climate — work that demanded rigor, evidence, and long-horizon thinking. That same discipline now shapes how he approaches infrastructure: as a system that has to hold up under real-world pressure, not just pass a demo.
He is a Kubestronaut, holding the CNCF's full Kubernetes certification track, and has built production systems in Java, Go, and Rust. He has also built two AI tooling projects and writes about infrastructure and systems design.
Field notes
Six practical checks to uncover security gaps in a running Kubernetes cluster, from image scanning and RBAC to Secrets, policy enforcement and runtime detection.
Why growing teams need an automated Kubernetes platform with repeatable deployments, built-in security, observability and cost controls.
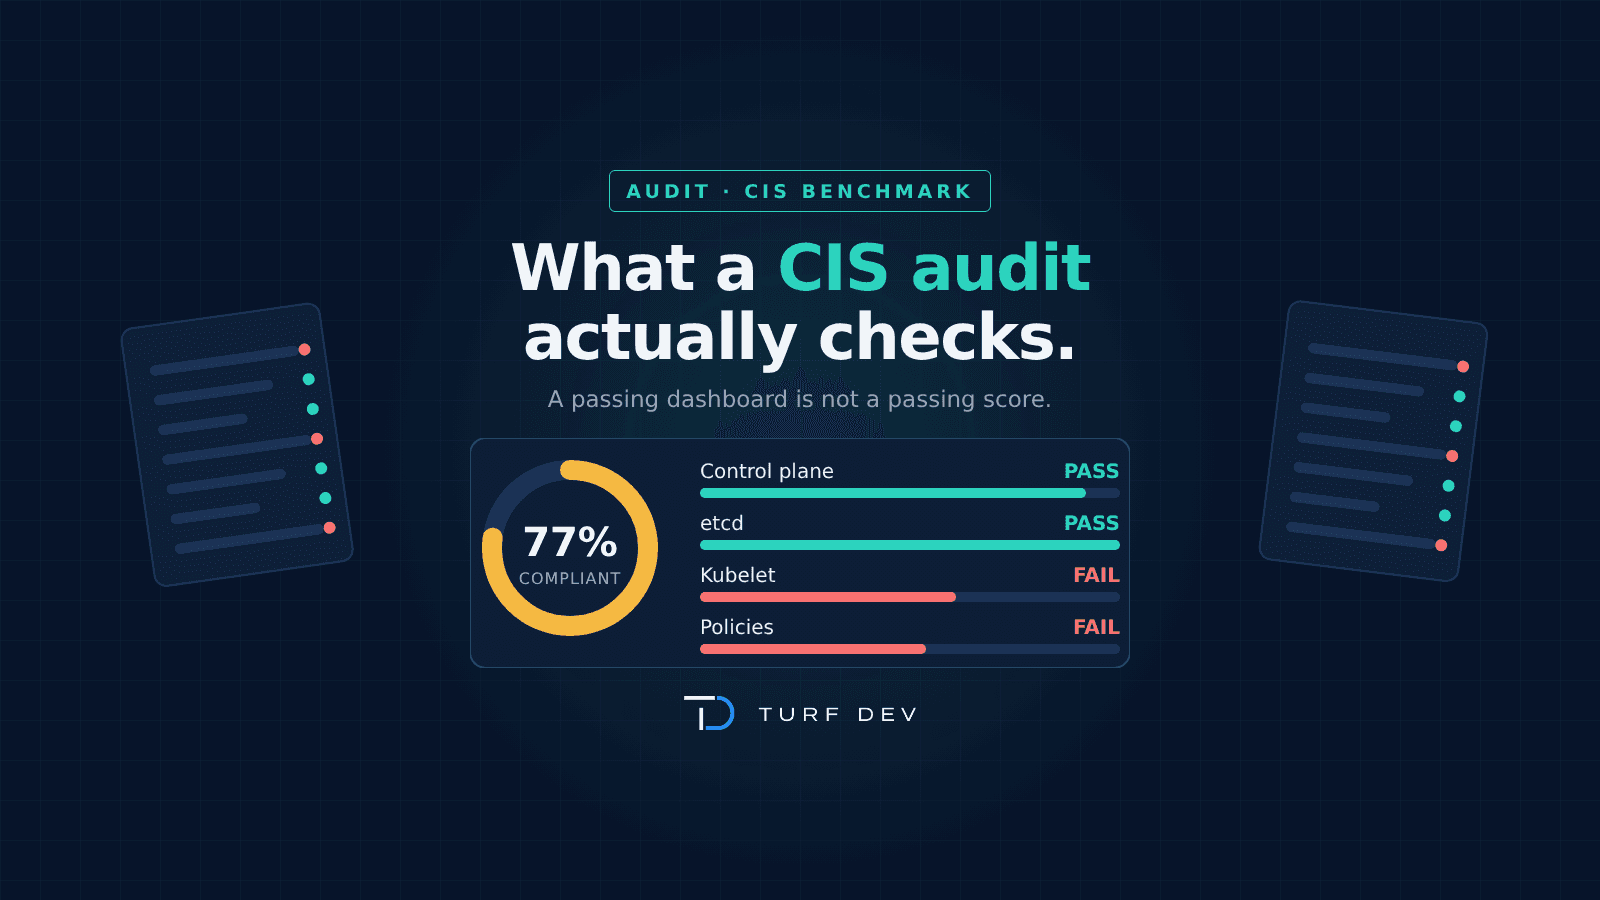
What a CIS Kubernetes audit checks across the control plane, etcd, worker nodes and security policies—and how to turn findings into a practical remediation plan.
Platform Mandate
Review platform posture, reliability constraints, and cost governance priorities with an infrastructure engineering team.