What a CIS Kubernetes Benchmark Audit Actually Checks
What a CIS Kubernetes audit checks across the control plane, etcd, worker nodes and security policies—and how to turn findings into a practical remediation plan.
A cluster isn't secure or insecure in the abstract. It is compliant or non-compliant against a specific set of controls. The CIS Kubernetes Benchmark is the most widely used baseline for that, and it is worth knowing what it inspects before you commission or run an audit.
What the CIS Kubernetes Benchmark is
The Center for Internet Security (CIS) publishes benchmarks: detailed, consensus-built configuration checklists. The Kubernetes benchmark groups its checks by component and marks each as automated or manual.
Managed services have their own versions, such as the CIS Amazon EKS, Google GKE and Azure AKS benchmarks. These skip the parts the cloud provider controls and focus on what you still own.
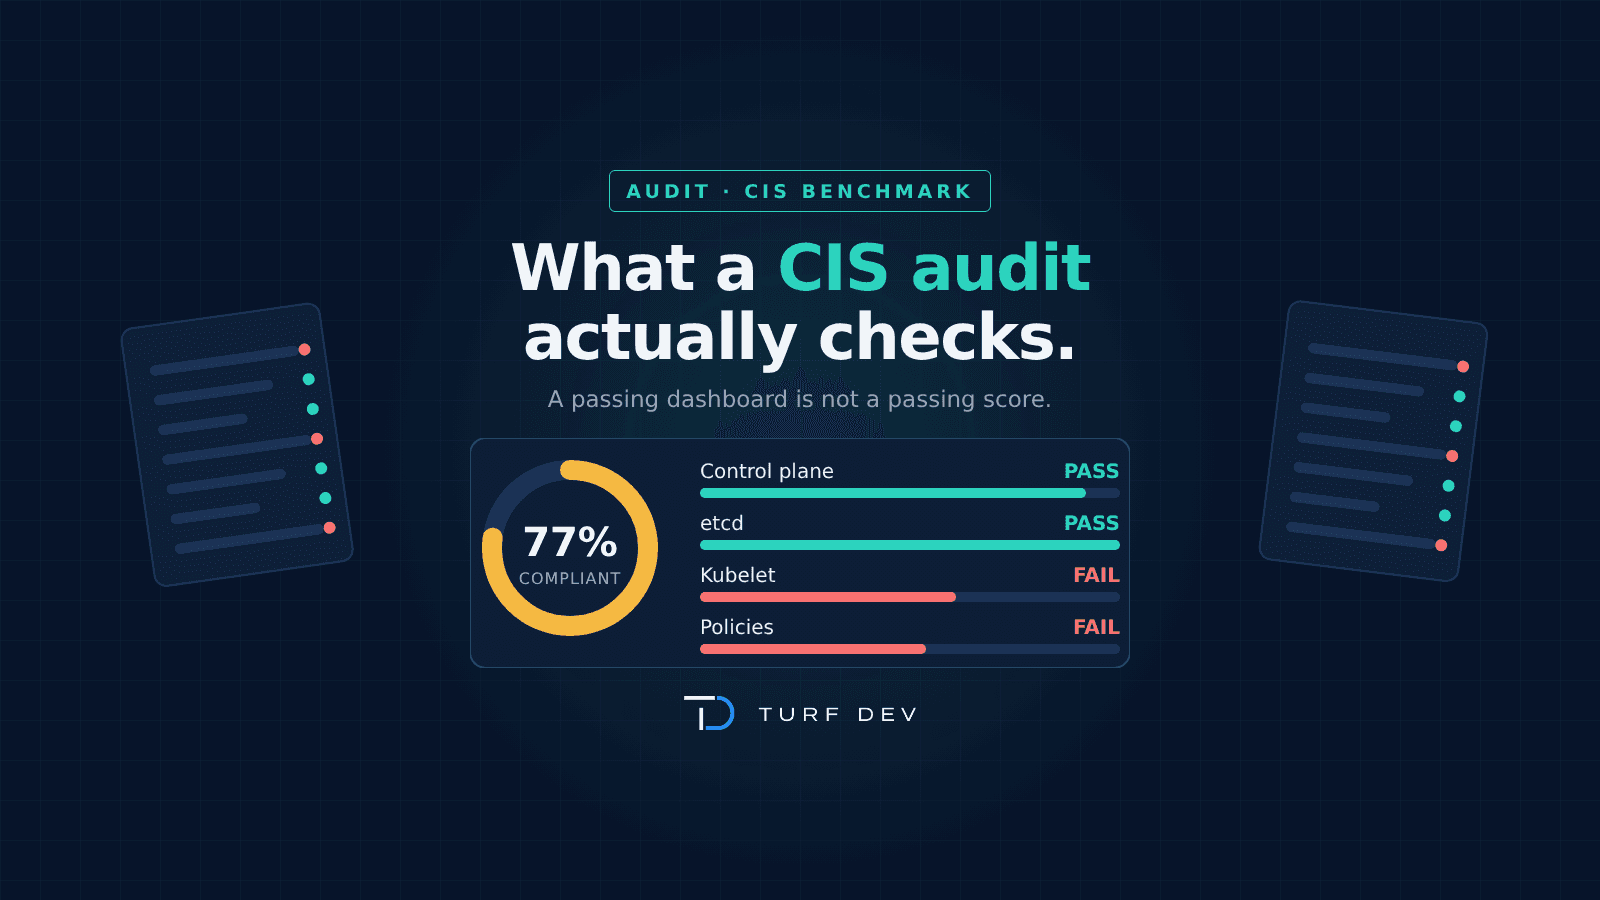
The four areas a CIS audit checks
1. Control plane components
The audit checks how the API server, controller manager and scheduler are configured. Typical findings:
Anonymous authentication left enabled on the API server.
Audit logging not configured, so there is no record of who changed what.
Admission controllers missing or misconfigured.
Many clusters still run defaults that were reasonable years ago but no longer are.
2. etcd
etcd stores every Secret in the cluster, so it gets close attention:
Is encryption at rest configured?
Do clients and peers authenticate with certificates?
Is etcd reachable from outside the control plane network?
3. Worker node configuration
The kubelet on every node is checked individually:
Anonymous authentication on the kubelet API.
The authorization mode (it should not allow every request).
The read-only port, which exposes pod information without authentication.
On EKS, GKE and AKS much of this is handled for you. On self-managed or on-prem clusters such as kubeadm or RKE2, this risk is entirely yours.
4. Policies: RBAC, Pod Security and network
This is where most of the real backlog sits, and where standard dashboards show nothing:
Wildcard RBAC roles and unnecessary cluster-admin bindings.
Service accounts with far more rights than they use.
Namespaces with no NetworkPolicy, so every pod can reach every other pod.
Privileged containers or pods running as root.
How to run a first check yourself
kube-bench, an open-source tool from Aqua Security, runs the CIS checks as a Kubernetes Job. Start it with:
kubectl apply -f https://raw.githubusercontent.com/aquasecurity/kube-bench/main/job.yamlThen read the results:
kubectl logs job/kube-benchEach check comes back as PASS, FAIL or WARN, with a remediation hint for every failure.
What a CIS score actually means
A CIS-aligned score is a point-in-time snapshot of how much of a defined, severity-weighted control set you satisfy. The number on its own matters less than what sits behind it: a prioritised backlog of exactly what to fix, in order of risk.
That backlog is what makes remediation predictable. You know the scope, so the work can be planned and priced instead of left open-ended.
Why we keep Audit and Harden separate
At Turf Dev, Audit and Harden are separate engagements, on purpose:
Independence: an auditor who also fixes the findings can't credibly mark their own work.
Clear scope: hardening against a scored backlog has a defined end. Hardening without one never finishes.
Proof: a rescan after hardening shows the score moved, with evidence.
How Turf Dev can help
Turf Dev's Kubernetes audit maps your cluster against the CIS Benchmark, adds the policy review that automated tools miss, and hands you a severity-ranked fix list. When you are ready, we harden against it and rescan to prove the result. Reach out at turfdev.in.
Discussion
Have a question or something to add? Share it below.
No comments yet. Be the first to join the discussion.